See Everything. Secure Everything.
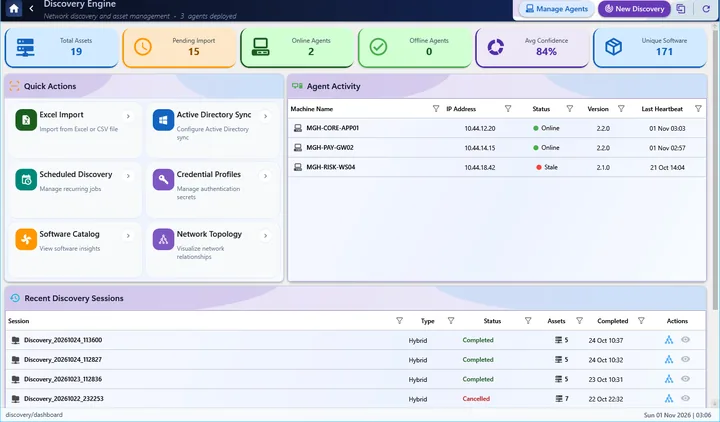
The ExGear Discovery Agent transforms your infrastructure into a living, breathing security dashboard. Automated discovery, real-time monitoring, and AI-driven insights—all feeding directly into your GRC workflows.
The Visibility Gap
Most GRC platforms rely on manual data entry and periodic assessments. By the time risks are documented, your environment has already changed.
Manual Inventories
Spreadsheets go stale the moment they're saved. Security teams spend hours updating asset lists that are outdated before the next audit.
Point-in-Time Scans
Vulnerability assessments run weekly or monthly miss critical exposures. Attackers don't wait for your scan schedule.
Disconnected Tools
Security data lives in silos—SIEM, EDR, CMDB, GRC. Connecting the dots requires manual correlation and delays response.
Introducing System Library Intelligence
A lightweight agent that lives on your endpoints, continuously collecting, analysing, and feeding intelligence directly into your GRC platform.
How It Works
Silent agent installation via Group Policy, SCCM, or script. Zero user disruption, minimal footprint.
Specialized collectors gather security configs, vulnerabilities, identities, and assets on a configurable schedule.
The analysis engine correlates findings, flags suspicious patterns, and calculates risk scores — enriched with AI-generated risk context.
Insights flow into risks, controls, and audit findings. Automated alerts trigger workflows before breaches occur.
Continuous Loop
Unlike point-in-time tools, the Discovery Agent creates a continuous feedback loop—adapting to your environment as it changes.
Comprehensive Collector Suite
Purpose-built collectors for every aspect of endpoint security and compliance.
Security Configuration
Complete visibility into security posture.
- Windows Firewall profiles & rules
- Defender status & signature age
- BitLocker encryption state
- UAC & privilege settings
- Password & audit policies
Vulnerability Indicators
Proactive weakness detection with CVE mapping.
- SMBv1 (EternalBlue exposure)
- RDP without NLA
- PrintNightmare vectors
- LLMNR poisoning exposure
- Unquoted service paths
Certificate Inventory
Never be surprised by an expired cert again.
- All certificate stores scanned
- Expiration tracking & alerts
- Weak crypto detection (SHA1)
- Private key presence
- Trust chain validation
Identity & Access
Know who has access and when they last used it.
- Local users & groups
- Admin group membership
- Stale account detection (90+ days)
- Active session tracking
- Password policy violations
Scheduled Tasks
Detect persistence mechanisms and rogue automation.
- Task inventory with actions
- Encoded PowerShell detection
- Internet download patterns
- Run-as-SYSTEM tasks
- Suspicious timing patterns
Browser Extensions
Shadow IT visibility in the browser layer.
- Chrome, Edge, Firefox coverage
- Permission analysis
- Risk scoring per extension
- Unapproved extension detection
- Data exfiltration risks
Database Instance Discovery
Automatically discover and inventory database instances across your estate.
Real-Time Monitors
Continuous change detection for critical system components.
AI-Powered Risk Intelligence
Raw data becomes actionable intelligence through machine learning and contextual analysis.

Anomaly Detection
Continuous detection rules baseline your environment and flag risky changes before they become incidents.
- Configuration baselines per endpoint
- Drift detection for configurations
- Stale account & active session alerts
- Privileged access indicators
Risk Scoring Engine
Every finding is scored based on exploitability, impact, and your specific context.
- CVE-mapped severity ratings
- Asset criticality weighting
- Exposure window calculation
- Control effectiveness adjustment
GRC Integration
Findings automatically link to your risk register, control library, and audit programs.
- Auto-create risks from critical findings
- Map to existing controls
- Generate audit evidence
- Feed compliance dashboards
Remediation Guidance
Expert-curated remediation commands with AI-generated risk context for every finding.
- PowerShell/GPO commands ready to run
- Prioritised remediation queue
- AI-drafted risk impact narratives
- Verification steps for each fix
Measurable Impact
What System Library Intelligence is engineered to deliver.
Asset inventory time reduced from weeks to hours
Audit findings reduced through proactive detection
Continuous monitoring vs. periodic assessments
Every collection timestamped and versioned
Cross-Platform Coverage
One platform, every endpoint type.
Windows
Full coverage for Windows 10/11, Server 2016+
Linux
Ubuntu 20.04+ and RHEL 8+
Cloud & Network
Agentless discovery via Active Directory, network scanning, and cloud APIs
Ready to See Everything?
Deploy the Discovery Agent and transform your security posture in days, not months. Complete visibility, continuous compliance, zero blind spots.