One Platform. Every Assurance Domain.

Nineteen modules sharing one risk universe, one control library and one evidence base. Every screenshot below is the product itself; select one to see it full size.

Audit, Risk & Compliance

The assurance core: one risk universe, one control library and one evidence base that every other module builds on.

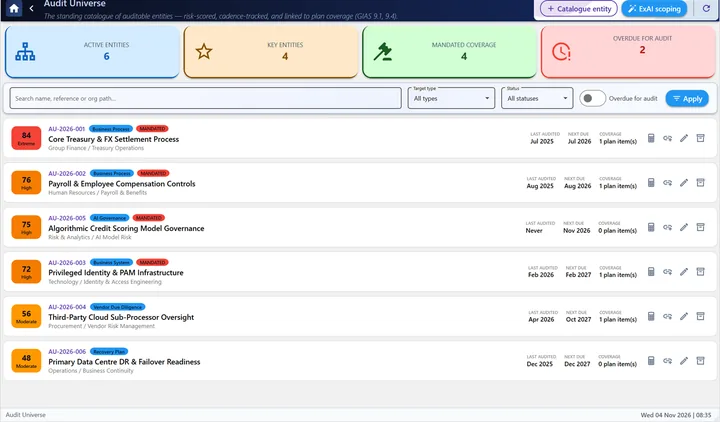
Audit Universe listing risk-scored auditable entities with plan coverage

Audit Management

The whole internal audit lifecycle, from a risk-scored audit universe to findings follow-up, aligned to the IIA’s Global Internal Audit Standards.

  • Audit universe with risk scores, cadence and plan coverage
  • Annual plans, schedules and resource management
  • Engagement workbench with review notes, sign-off and engagement chat
  • Findings register and follow-up action tracking
  • QAIP & conformance assessments
Explore Internal Auditing
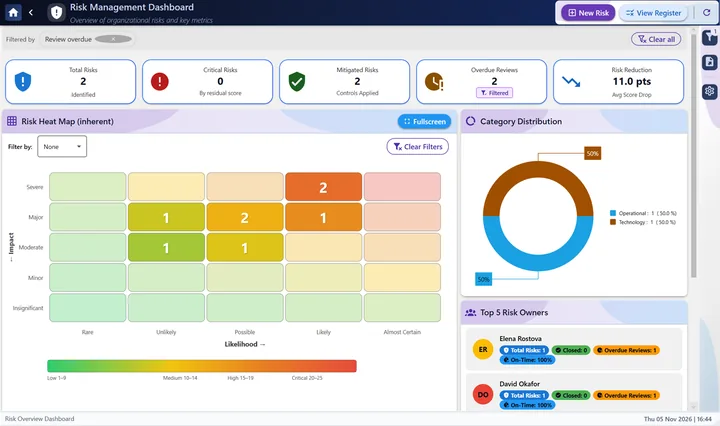
Risk Management dashboard with the inherent risk heat map, category distribution and top risk owners

Risk Management

An enterprise risk register with scoring, appetite and treatment, linked to the controls and indicators that manage each risk.

  • Risk register with inherent and residual scoring
  • Heat map, risk network and risk insights
  • Treatment plans with approval, actions and effectiveness tracking
  • Residual-score advisory and configurable scoring
Explore GRC
Compliance Tracking dashboard with posture, executive KPIs and a 12-month compliance trend

Compliance Management

Track obligations, frameworks, policies and attestations in one place, with coverage calculated from your implemented controls.

  • Regulatory obligations register with monitored sources
  • Framework coverage and Statement of Applicability
  • Policy library with approvals, exceptions and attestation campaigns
  • Assessment workspace, compliance calendar and monitoring console
Explore GRC
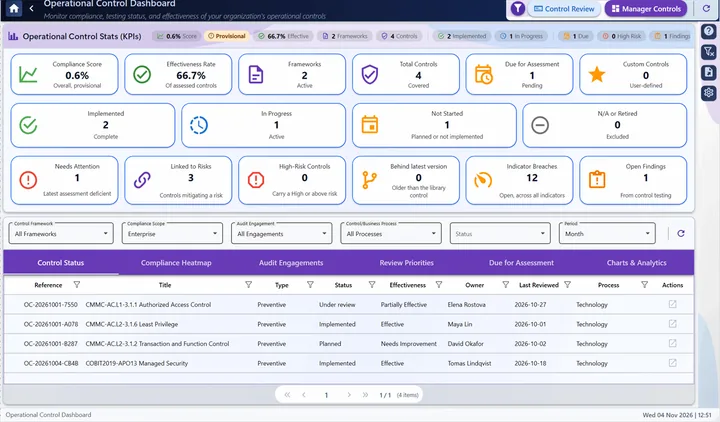
Operational Control dashboard with compliance score, effectiveness rate and control status

Control Management

A versioned control library mapped to standards, and the operational controls your teams actually run and test.

  • Control library and control standards with mappings
  • Operational controls with assessment and effectiveness tracking
  • Control review cycles and change proposals
  • Links to risks, processes, findings and indicators
Explore GRC

Operations & Resilience

The modules that run day-to-day assurance across processes, technology, suppliers and people.

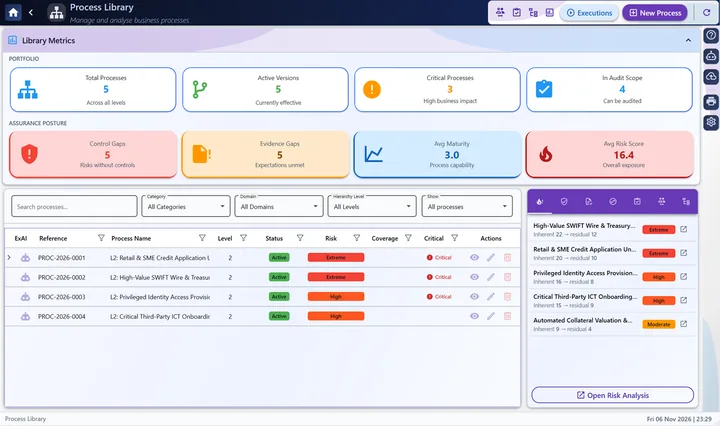
Process Library register with portfolio metrics, assurance posture and risk ratings per process

Process Library

Document business processes once and see their risks, control coverage and evidence quality together.

  • Process register with hierarchy, versions and recertification
  • Risk analysis and control coverage with gap detection
  • Evidence assurance, executions and change impact
  • Segregation-of-duties rules and process templates
Explore the Process Library
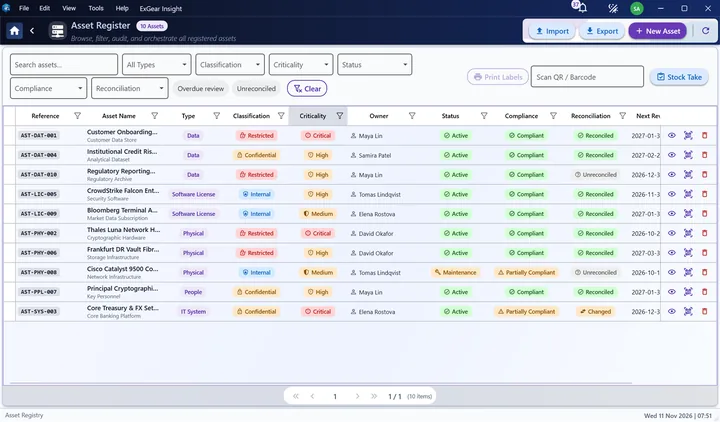
Asset Register grid with classification, criticality, compliance and reconciliation status

Asset Management

A governed register for every managed asset, reviewed on a cycle and verified in the field.

  • Asset register with classification, criticality and lifecycle
  • Review cycles and reconciliation against discovered assets
  • QR and barcode stock takes with the mobile companion app
  • Bulk import and label printing
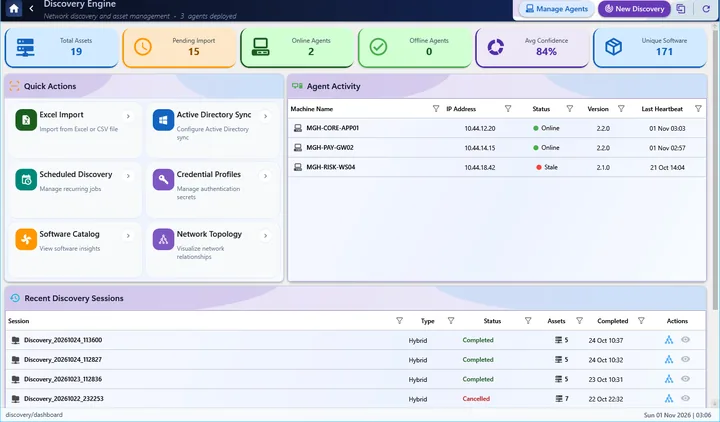
Discovery Engine with discovered assets, agent activity and recent discovery sessions

IT Systems & Discovery

Know what you run. A system library fed by discovery agents and network discovery, with the security posture of every monitored machine.

  • System library with criticality, lifecycle and ExAI analysis
  • System relationship graph with critical-path and impact views
  • Discovery agents, scheduled discovery and Active Directory sync
  • Agent Security Insights: fleet score, findings and collectors
  • Capacity management
Explore IT Systems & Discovery
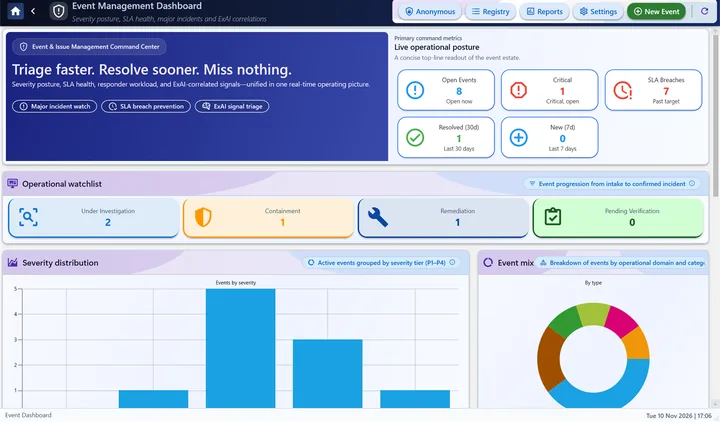
Event Management dashboard with open events, SLA breaches, operational watchlist and severity distribution

Event & Issue Management

Capture events and issues from any channel, triage them against SLAs and drive them to verified closure.

  • Event registry, quick console and guided report wizard
  • Anonymous reporting
  • Problem registry and corrective actions
  • Escalation management and SLA settings
  • Major incident war room
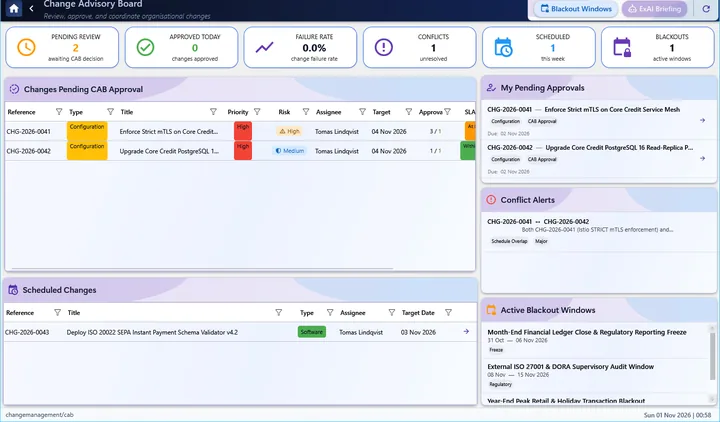
Change Advisory Board dashboard with pending approvals, conflict alerts and active blackout windows

Change Management

One lifecycle for application, configuration and regulatory change, with the approvals and evidence to prove it was controlled.

  • Change requests, releases and a change calendar
  • Change Advisory Board with conflict alerts
  • Blackout windows with exemption requests
  • Approval workflows, evidence checklists and release gates
  • Regulatory change tracking and configuration baselines
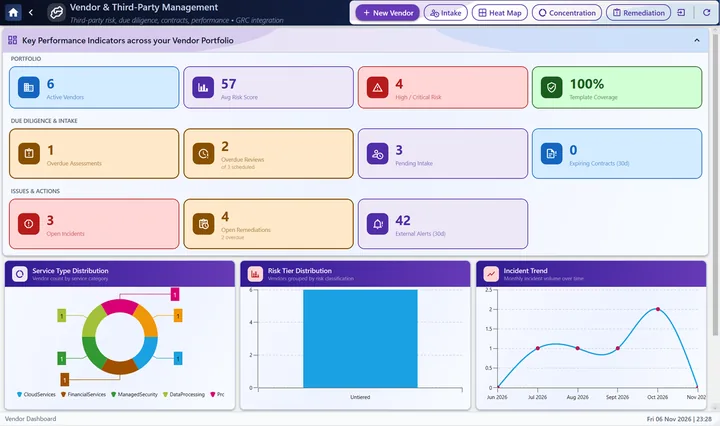
Vendor and Third-Party Management dashboard with portfolio KPIs, due diligence and incident trend

Vendor & Third-Party Management

The vendor lifecycle from intake to offboarding, with due diligence, performance and concentration risk in view.

  • Vendor registry, intake requests and onboarding
  • Due diligence with reusable templates and remediation tracking
  • Contracts, SLAs and performance scorecards
  • Risk heat map and concentration analysis
  • Vendor incidents and structured offboarding
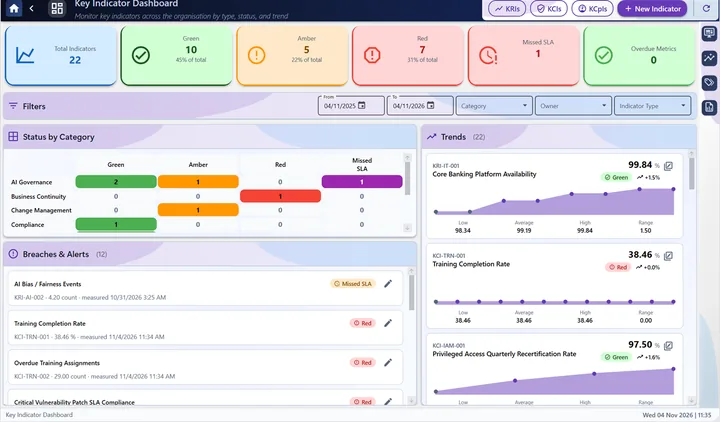
Key Indicator dashboard with status by category, trends and breaches

Key Indicators

KRIs, KCIs, KPIs and more in one indicator library, with bands, breaches and trend history across every domain.

  • Indicator library with metric bands and templates
  • Breach workspace with alerts and follow-up
  • Cross-domain posture and assurance consistency
  • Data ingestion bindings with ingestion health
  • Unified indicator reports
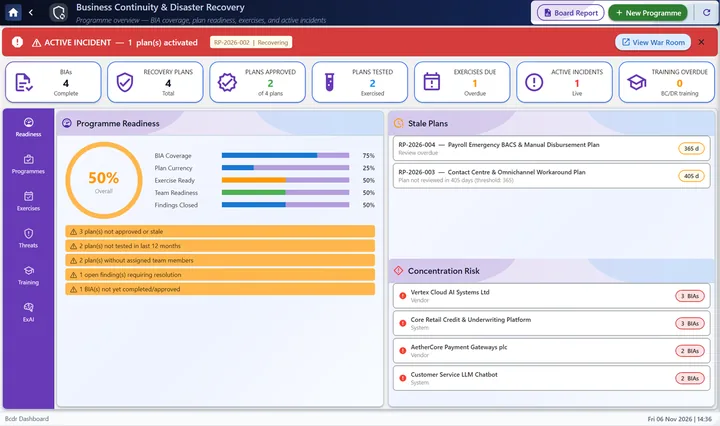
Business Continuity and Disaster Recovery dashboard with programme readiness, stale plans and concentration risk

Business Continuity & DR

Business impact analysis, recovery plans and exercises, with live incident activation when it counts.

  • Business impact analyses and versioned recovery plans
  • Exercise management and incident activations with a war room
  • Dependency graph and disruption simulator
  • Concentration and fourth-party risk
  • BCMS audits, management reviews and board reports
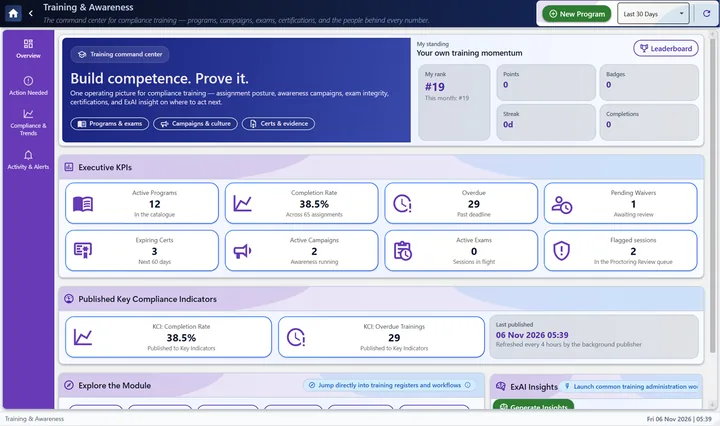
Training and Awareness dashboard with executive KPIs, completion rate and published compliance indicators

Training & Awareness

Compliance training that can prove competence: programmes, exams, campaigns and certifications with an audit trail.

  • Training programmes, assignments and learning paths
  • Question bank, exams and proctoring review
  • Awareness campaigns and leaderboard
  • Certifications, waivers and the training matrix

Governance, Legal & AI

Enterprise modules for the board’s own agenda.

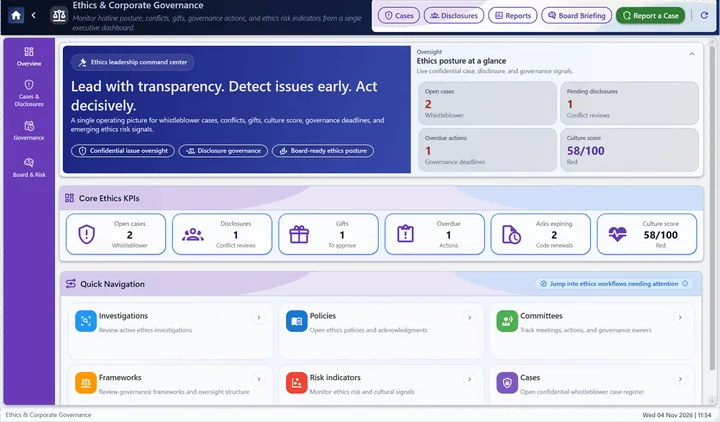
Ethics and Corporate Governance dashboard with whistleblower cases, disclosures and culture score

Ethics & Corporate Governance

The conduct layer of your control environment, from the whistleblower line to the board committee.

  • Whistleblower cases and investigations
  • Conflicts of interest, gifts and entertainment registers
  • Ethics policies with acknowledgements
  • Board committees and governance frameworks
  • Ethics risk indicators
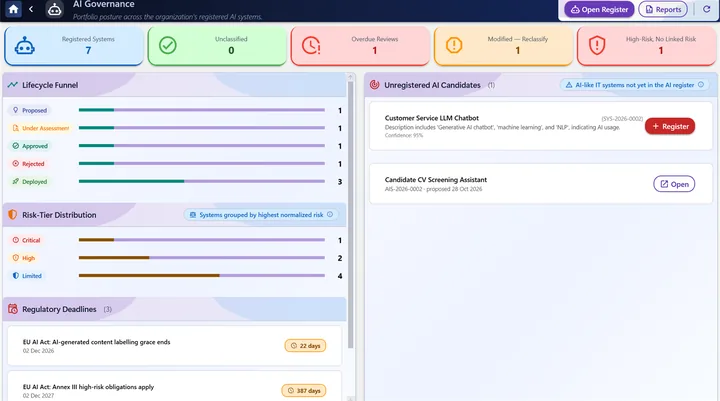
AI Governance dashboard with lifecycle funnel, risk-tier distribution and regulatory deadlines

AI Governance

A register of the AI systems you build and buy, classified by risk and tracked against the standards that apply.

  • AI system register with intake, classification and conformity
  • AI standards library with requirement tracking
  • Review templates and monitoring plans
  • AI incidents and regulatory deadlines
  • Unregistered AI candidates surfaced from the system library

In Every Package

Evidence, reporting and planning run underneath every other module, so every package includes them.

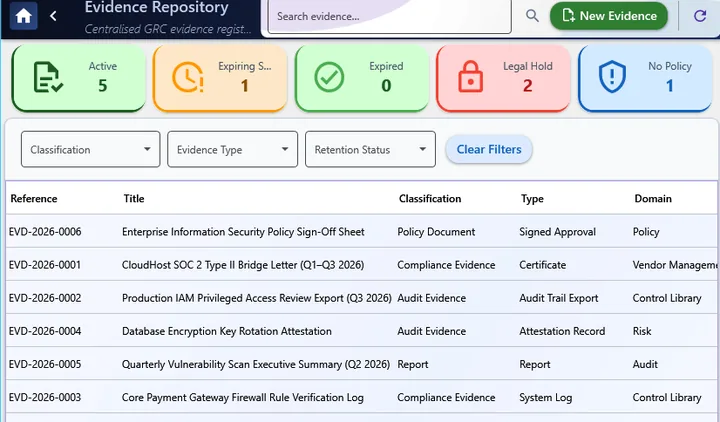
Evidence Repository list with classification, type and domain for each record

Document & Evidence Management

The authoritative home for GRC evidence, from request to retention.

  • Evidence repository and collections
  • Evidence request campaigns with a fulfilment queue
  • Retention policies and legal holds
  • Links to audits, risks, controls and policies
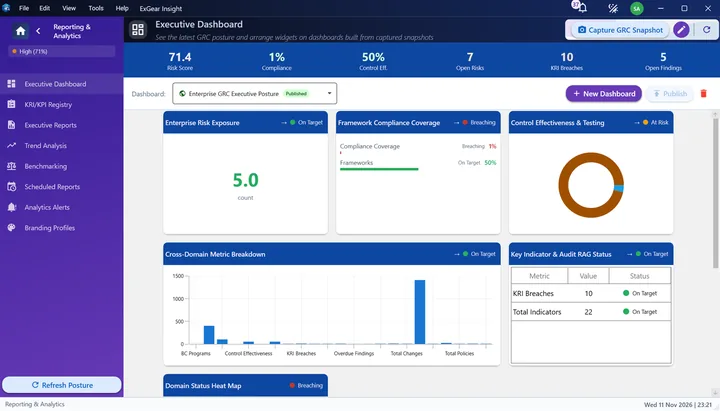
Executive Dashboard in Reporting and Analytics with risk exposure, compliance coverage and RAG status widgets

Reporting & Analytics

Board-grade reporting from live data, with dashboards you arrange yourself.

  • Executive dashboards built from GRC snapshots
  • Executive report packages with review and optional ExAI narrative
  • KRI/KPI registry, trend analysis and benchmarking
  • Scheduled reports, analytics alerts and branding profiles
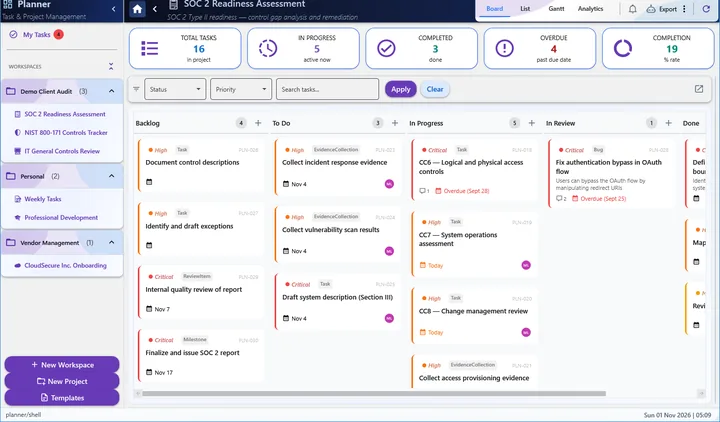
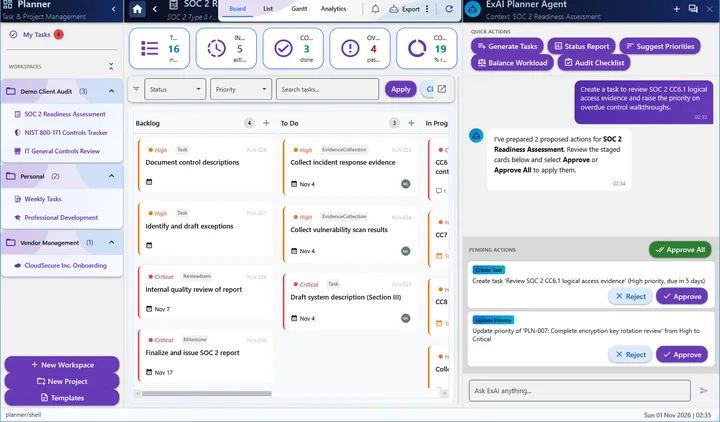
Planner board for a SOC 2 readiness project with backlog, to do, in progress and in review columns

Planner

Personal and team work management that is natively linked to your GRC records.

  • Board, list, Gantt and analytics views
  • Workspaces, projects and templates
  • My Tasks across every project
  • ExAI Planner agent that proposes actions for your approval

Across Every Module

The same assistant, the same companion app and the same access rules, wherever you are working.

ExAI Planner agent proposing two task actions, each with Approve and Reject buttons

ExAI, the built-in assistant

ExAI drafts, analyses and suggests inside the module you are working in. It proposes; you approve.

  • Suggestions you review and accept, never silent changes
  • Action cards in the Planner and Audit Schedule that wait for your approval
  • Sees only what the signed-in user is allowed to see
  • Administrator controls for provider, allowance and usage
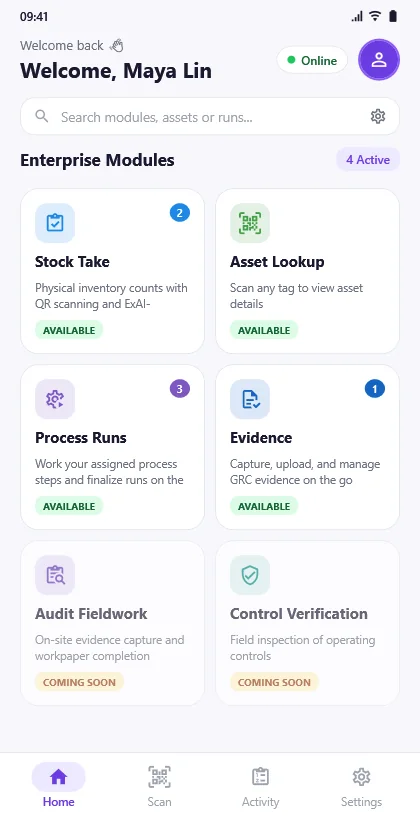
Mobile companion app home screen with Stock Take, Asset Lookup, Process Runs and Evidence modules

Mobile companion app

Take the fieldwork with you. The companion app shows only the modules your package and your administrator allow.

  • Stock takes with QR and barcode scanning
  • Asset lookup from any tag
  • Process runs assigned to you
  • Evidence capture and upload on the go
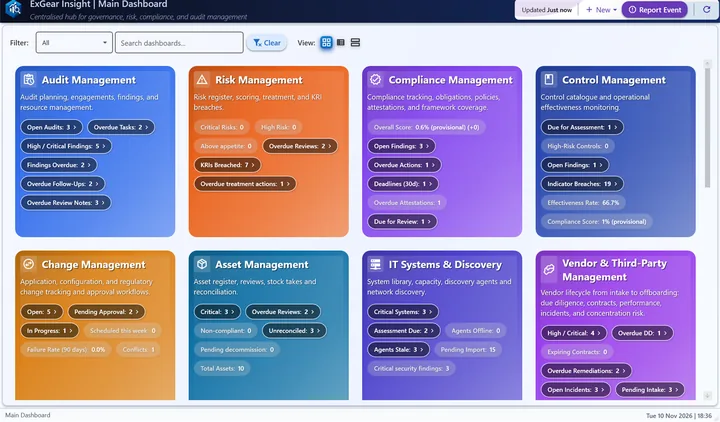
Main Dashboard showing only the module tiles this organisation and user can open

Access that follows your package and your people

The Main Dashboard shows each person the modules their organisation has bought and their role lets them open, and nothing else.

  • Modules switch on with your package, with no reinstall
  • Domain access by department, with per-user overrides
  • Roles and individual permissions
  • Notices by e-mail, text message and Microsoft Teams channel
Compare packages

On the Roadmap

Designed and specified — coming to the platform next.

ESG & Sustainability

GRI, SASB, ISSB (IFRS S1/S2), CSRD/ESRS, and TCFD reporting with cross-standard mapping — report once, satisfy many.

Pen Testing & Vulnerability

Ingest findings from Nessus, Qualys, and Burp; AI triage and deduplication; SLA-driven remediation tracking.

SBOM Governance

CycloneDX and SPDX ingestion, component-to-vulnerability matching, and license compliance for your software supply chain.

Go Deeper

Detailed pages for the audit and GRC core, the libraries and the full feature list.

See the Full Platform in Action

One integrated data model across every module — risks, controls, evidence, and reporting that finally agree with each other.